
CISA adds Cisco Catalyst SD-WAN Manager vulnerability to its Known Exploited Vulnerabilities catalogue
The US agency CISA has added CVE-2026-76504, a vulnerability in Cisco Catalyst SD-WAN Manager, to its catalogue of actively exploited flaws. This is the latest in a series of edge network equipment vulnerabilities identified throughout September.
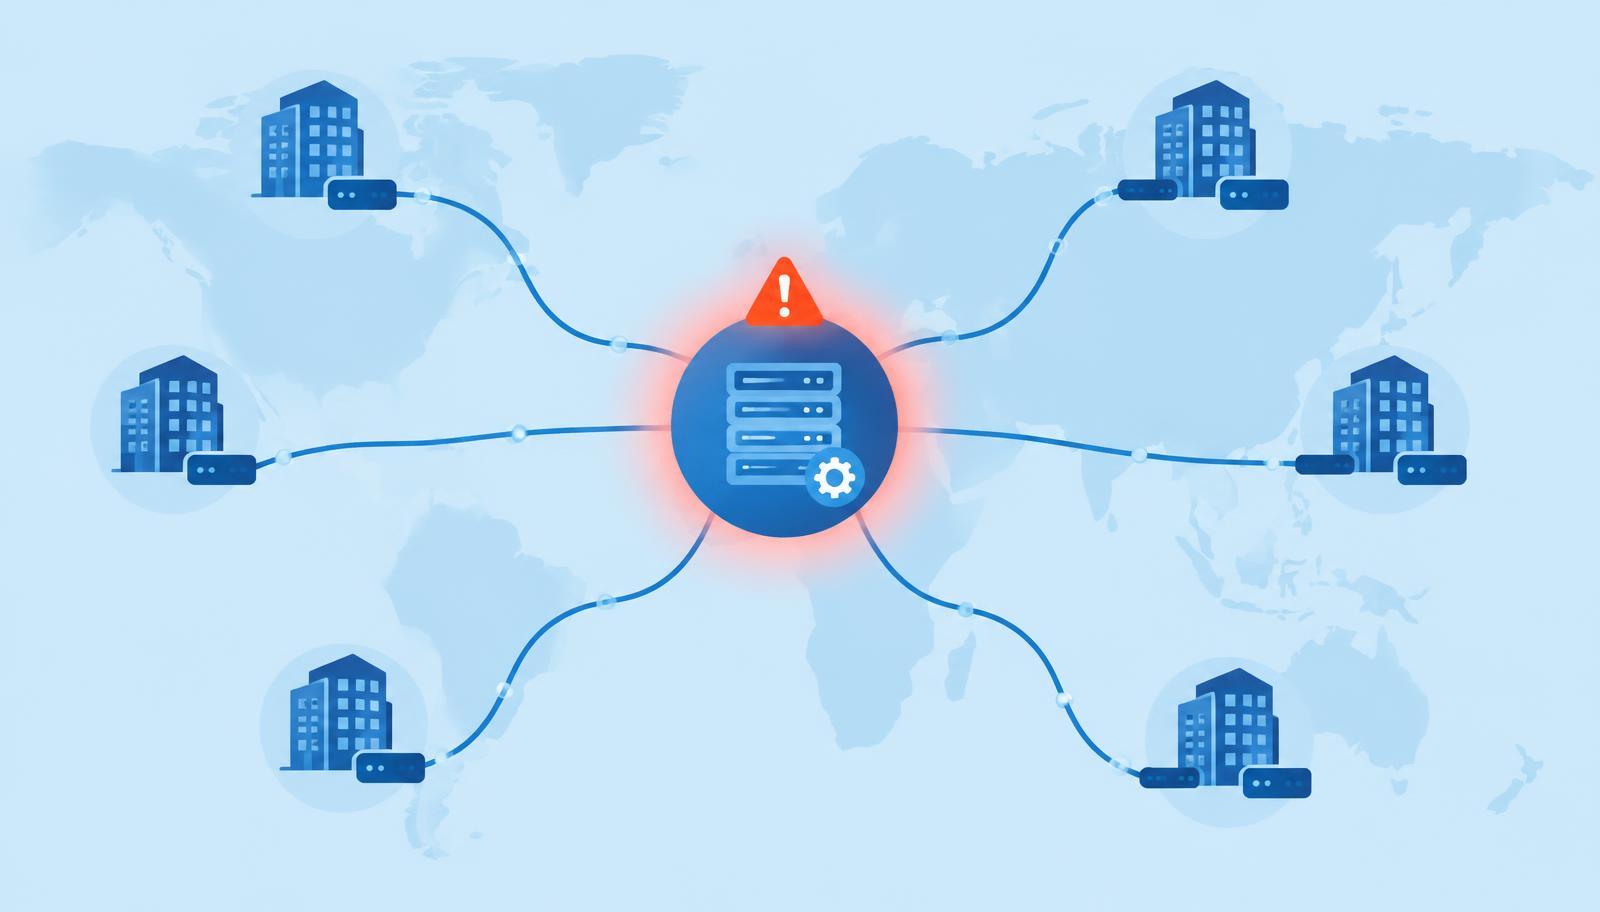
News summary
On 30 September 2026, CISA added CVE-2026-76504 to its Known Exploited Vulnerabilities (KEV) catalogue, describing it as a hexadecimal encoding flaw in Cisco Catalyst SD-WAN Manager. Inclusion in this list confirms that there is evidence of active exploitation.
SD-WAN Manager serves as the orchestrator for an enterprise wide area network, defining site connectivity, policy application, and traffic routing. A compromise at this level does not merely affect an isolated device, but potentially the configuration of the entire corporate network.
This alert follows a particularly intense month for network perimeters. On 22 September, CISA added four flaws from Check Point, Arista VeloCloud, and F5 in a single update, followed by an alert regarding two zero-days in Citrix NetScaler on 27 September. The pattern is evident: attackers are targeting the equipment that manages remote access and inter-site connectivity.
While CISA mandates only apply to US federal agencies, its catalogue is a vital benchmark for any organisation prioritising patch management. Businesses using Cisco SD-WAN should consult the manufacturer's official advisory to identify affected versions and available fixes.
Source: CISA — 30 September 2026
Frequently Asked Questions
- What does it mean when a vulnerability is in the KEV catalogue?
- It means CISA has evidence that the flaw is being exploited in real-world attacks. This serves as a signal to treat its remediation as a high priority rather than a routine preventive task.
- Does this affect companies not using Cisco SD-WAN?
- Not directly. However, the trends observed this month show that any perimeter equipment —VPN, firewalls, or SD-WAN— is a primary target and must be kept updated.
Concepts mentioned in this article: Cloud · Patch management · Vulnerability
Perimeter equipment is currently a top target for attackers. At Seintec, we audit your network, prioritise critical patches, and secure your management consoles. Speak with our cybersecurity team.
Contact SeintecRelated service
Cybersecurity
We shield your business so it never stops.