AWS separates firewall and IPS controls in new policies
AWS introduces a new NGFW policy model for Network Firewall. The change separates access and intrusion prevention rules; existing policies continue to work.
News summary
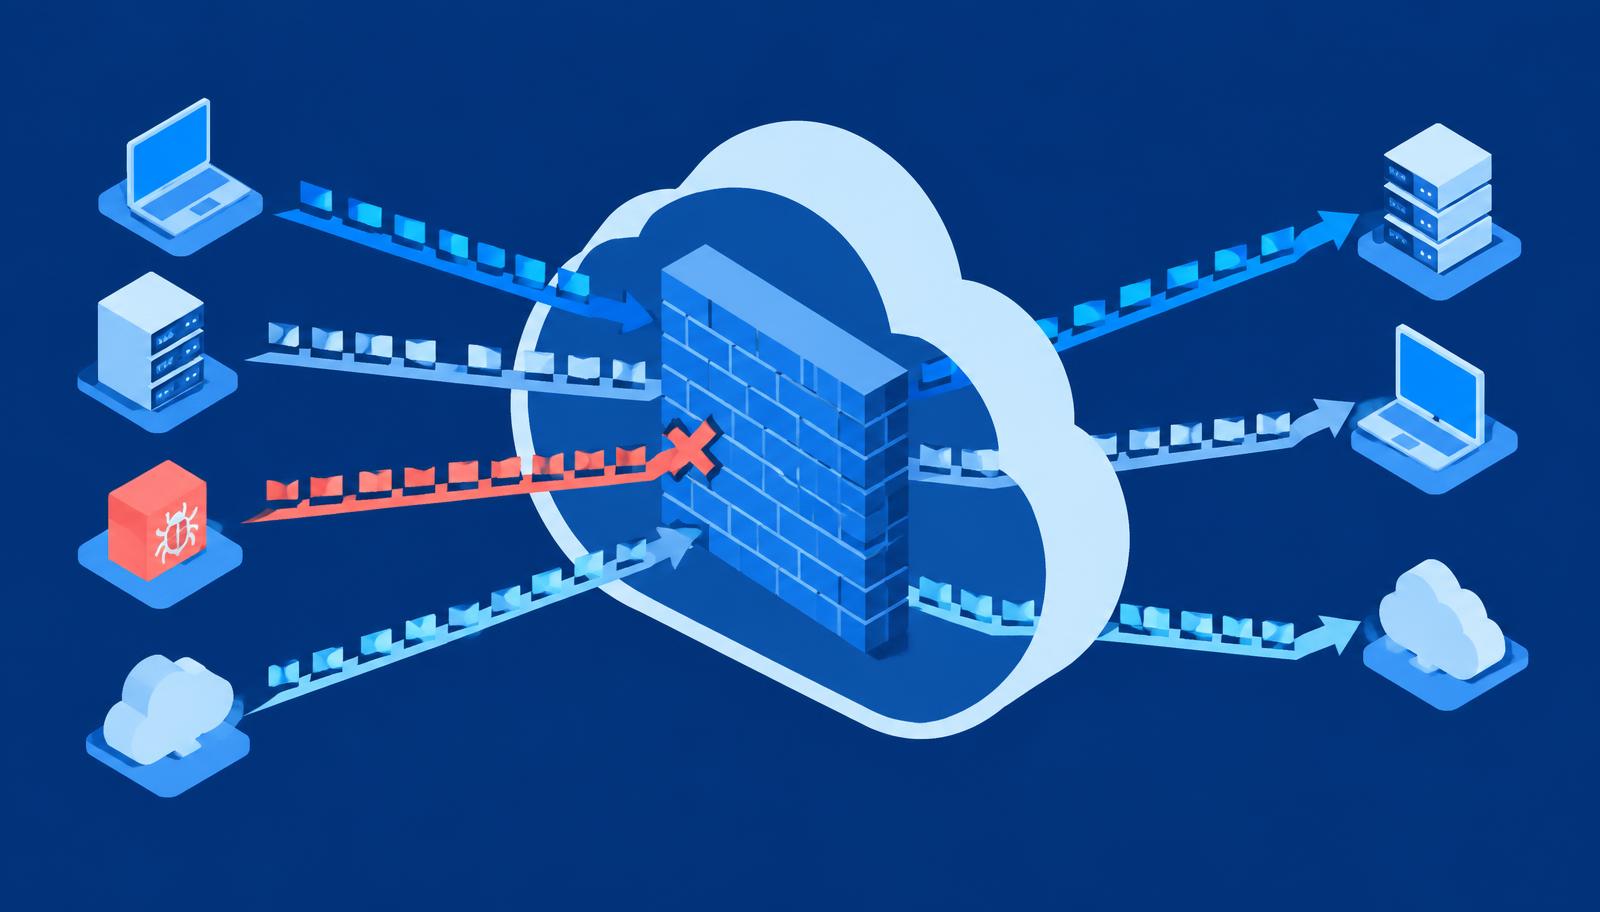
On 10 November, AWS announced a new next-generation firewall policy model for AWS Network Firewall. The provider explains that access rules and intrusion prevention rules are organised into separate layers, each with its own capacity. Existing policies continue to operate unchanged.
The new model allows access to be denied by default and combined with managed or custom IPS rule groups. According to AWS, the model's rules are stateful and are evaluated using the connection context. This does not make every configuration secure: an overly broad exception can still authorise unnecessary traffic.
For IT systems teams, the separation makes it easier to discuss two distinct questions: which communications the application needs and which threats should be detected or blocked within those communications. Migration requires tests of legitimate traffic and a review of the rules actually being applied.
Source: AWS — 10 November 2026
What to check in your business
Document the destinations and ports required for each application before changing policies.
- Test access and IPS rules separately with representative traffic.
- Review logs of blocked traffic and retain the previous policy for a controlled rollback.
Concepts mentioned in this article: Firewall
At Seintec, we work with you to review your systems' dependencies, access and continuity so you can prioritise improvements on an informed basis. Contact our team.
Contact SeintecRelated service
Cloud Services
Cloud services to scale your business.